HomeBlogApplication SecurityCore Banking Security: How to Secure Applications Without Disrupting Operations
Core Banking Security: How to Secure Applications Without Disrupting Operations
Why Core Banking Security Matters for Modern Banks
Core banking applications handle the work that keeps banking services running. Customer onboarding, account management, transactions, loan processing, payments and regulatory reporting all depend on these systems. When one of them has a security weakness, the impact can extend to customer data, financial activity and service availability.
The difficulty is that these applications rarely work in isolation. A core platform may be connected to mobile banking, internet banking, APIs, fintech services, cloud platforms and internal applications. A weakness in one of these connections can create a route into systems that hold sensitive financial information.
Banks also have to deal with a practical problem when improving security. A vulnerability may need to be fixed quickly, but taking a core system offline is rarely a simple option. Transactions still have to be processed, customers still need access to their accounts, and connected services have to keep working. Security testing and updates therefore need to be planned around the way these systems operate.
This is where core banking security needs a practical approach. Access should be controlled, application and API weaknesses should be identified early, sensitive information should be protected, and activity should be monitored closely. Security checks can also be brought into development and testing rather than waiting until an application is already in production.
Key Security Risks in Core Banking Applications
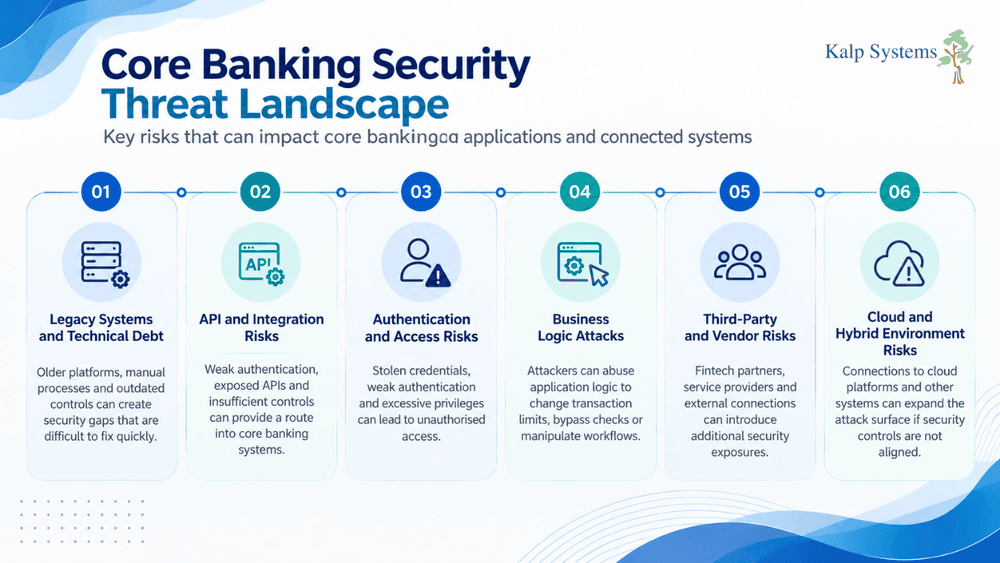
The risks around a core banking application are not limited to a single vulnerability. Older platforms can be difficult to change, while newer integrations bring APIs, external services and additional access points into the picture. A weakness in any one of these areas can create problems for the wider system.
Legacy Systems and Technical Debt
Some banks still run core banking platforms that were built years ago. These systems were designed for a different technology environment, so adding newer security controls can take time and careful testing.
Monolithic architecture is one example. A small change in one part of the application can affect another function that depends on it. Older encryption methods, hard-coded credentials and manual processes can create similar problems. Security teams may know that an update is needed, but making that change safely requires a good understanding of the system and its dependencies.
This is also why replacing a legacy platform is not always the immediate answer. In some cases, the safer option is to strengthen the existing system in stages while longer-term modernisation work continues.
API, Authentication and Business Logic Risks
APIs have become an important part of banking applications. They allow core systems to exchange information with mobile applications, internet banking platforms, fintech services and other connected systems. If an API has weak authentication or exposes more data than necessary, it can become an entry point for an attack.
Account credentials are another concern. Stolen credentials, weak authentication processes and session hijacking can give an attacker access to functions that normally belong to a legitimate user.
There are also attacks where the application itself is being used in an unintended way. An attacker might try to change a transaction limit, bypass a verification step or take advantage of a flaw in a payment or loan workflow. These business logic attacks can be difficult to identify because individual requests may appear legitimate.
Third-Party and Insider Threats
Core banking systems are connected to more than internal applications. Vendors, fintech partners, outsourced development teams and other service providers may have access to systems or data. A weakness on one side of that connection can create a problem for the bank as well.
Internal access needs the same level of attention. Users with excessive privileges can reach functions or information that they do not actually need for their role. If an account is compromised, those unnecessary permissions can increase the damage.
Access should therefore be reviewed according to what a user, service or partner actually needs. Third-party connections also need appropriate security checks instead of being treated as trusted simply because they are part of an existing relationship.
Core Banking Security Controls for Continuous Protection
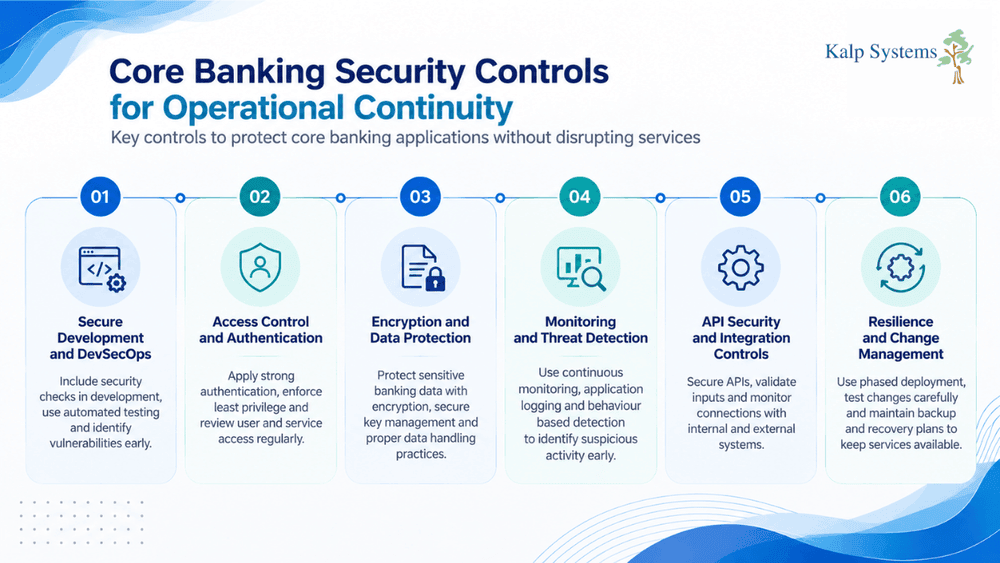
Security controls for a core banking application have to work alongside normal banking operations. A control that creates too much friction can become difficult to maintain, especially when the application is processing transactions throughout the day.
This is why security needs to be built into different stages of the application, from development and access management to monitoring activity after deployment. Some controls can run in the background, while others need to be reviewed as part of normal development and change processes.
Secure Development and DevSecOps
Security testing is easier to handle when an application is being developed. Developers can check code for weaknesses, test new changes and deal with vulnerabilities before those changes reach a live banking environment.
DevSecOps supports this by bringing security checks into the development process. Code analysis and vulnerability testing can be included in CI/CD pipelines, alongside secure coding practices based on recognised application security guidance such as OWASP.
This also changes how security teams deal with vulnerabilities. Instead of waiting for a problem to appear after deployment, a weakness can be found while the relevant code is still being changed. That gives developers more opportunity to fix it without putting pressure on a live core banking service.
Access Control, Encryption and API Security
Access to a core banking application should be tied to what a person or service actually needs to do. An administrator may require broader permissions than a standard user, but even privileged access should have clear limits.
Strong authentication and least privilege can reduce the damage caused by compromised accounts. The same principle applies to applications and APIs that communicate with the core platform. An API should not automatically receive broad access simply because it belongs to a trusted internal or external service.
Data protection is another part of this control layer. Sensitive information should be encrypted when it is stored and when it is transferred between connected systems. Where different platforms or environments are involved, encryption keys also need proper management so that protection does not become inconsistent.
Continuous Monitoring and Threat Detection
A security test carried out once cannot show what is happening inside an application later in the day. Banking applications generate a large amount of activity, so unusual behaviour can appear between scheduled assessments.
Continuous monitoring gives security teams a way to watch that activity while the application remains in use. Runtime protection, application logs and behaviour-based detection can be used to identify activity that does not fit expected patterns.
For example, repeated failed access attempts, unusual application behaviour or activity around sensitive functions may warrant investigation. Security teams can correlate application logs with other relevant events to understand what happened and where the activity came from.
These controls can operate without stopping transaction processing, which is particularly useful for systems where regular downtime is difficult to accommodate.
Zero-Trust and Least Privilege
Core banking applications often have users, internal services, APIs, and third-party connections interacting with the same environment. Treating all of these connections as trusted can leave too much room for an attacker if one account or service is compromised.
A Zero Trust model takes a different approach. Access is checked according to the identity and context of the request, rather than being granted simply because the request originates from an internal network.
Least privilege works alongside this model. Users and services receive the permissions they need for their tasks, rather than access to unrelated functions. Access can then be reviewed and adjusted as requirements change. privilege works alongside this model. Users and services receive the permissions they need for their tasks, rather than access to unrelated functions. Access can then be reviewed and adjusted as requirements change.
For core banking systems, this helps keep sensitive functions behind additional checks without interfering with legitimate transactions and application activity. The original article similarly emphasises verification of users, devices and application interactions, together with least privilege and continuous validation.
Securing Legacy and Hybrid Core Banking Environments
Core banking environments often contain a mix of older and newer technologies. The main banking application may still run on an established platform, while mobile banking, APIs, analytics and other services have been added around it over time. This creates dependencies that need to be considered whenever a security change is planned.
Older platforms can have their own limitations, while cloud-connected applications introduce different access points and data flows. Security controls therefore need to cover the full environment, rather than focusing only on the core application.
Protecting Legacy Core Banking Systems
Some legacy banking platforms were designed at a time when the security requirements were different from those seen today. Hard-coded credentials, older encryption methods and manual processes can still be present, and changing them may require more work than it would in a newer application.
The difficulty is that the core platform is usually connected to other services. A change made to improve one security control could affect a payment process, reporting function or another application that depends on it.
For that reason, security teams need a clear view of these dependencies before making changes. Access to the platform can then be tightened, privileged accounts can be reviewed, and activity can be monitored more closely.
Where a legacy application cannot support a newer security feature, protection can also be added around it. This could include controls at the access, network or application layer. It gives the bank a way to reduce exposure without immediately replacing the underlying platform.
Security improvements can then be introduced gradually and tested alongside normal operations. This is particularly useful for core systems where an unexpected interruption can affect transactions and connected banking services.
Securing Hybrid and Cloud Connected Applications
Hybrid environments bring another set of considerations. A core banking application may remain on-premises while other services operate in the cloud. Data and requests then move between environments through APIs and other connections.
Those connections need to be controlled carefully. Identity based access can restrict which users and services are allowed to interact with the core platform. API gateways can provide another point for managing and monitoring traffic before it reaches the application.
Data protection also needs to continue across different environments. Encryption should cover sensitive information while it is stored and transferred, with appropriate key management in place.
Visibility can become difficult when monitoring tools are separated by the environment. An event in a cloud application may only make sense when it is viewed alongside activity from the core banking platform. Bringing relevant logs and security events together can make these relationships easier to identify.
This becomes particularly useful during an investigation. Instead of looking at the core application, API activity and cloud services separately, the security team can trace activity across the connected environment and determine where an unusual request originated.
For banks operating a mix of legacy and cloud-connected applications, the practical requirement is to strengthen these connections without creating unnecessary changes to the core transaction environment.
Core Banking Security, Compliance and Operational Resilience
For a bank, application security and compliance usually come together. The same weakness that exposes a customer record or allows unauthorised access can also raise questions during an audit or regulatory review.
Core banking systems therefore need controls that can be checked over time. Access records, security testing results, monitoring data and incident records are useful for this purpose. They show what has been done and, just as importantly, provide a record of what happened when a control was tested or an issue was found.
Keeping this information as part of regular security work is more practical than trying to collect everything when an audit is already due.
RBI and Data Protection Requirements
Core banking applications deal with financial information as well as personal data. Security controls need to be taken into account.
For banks operating in India, Core Banking Security in India needs to address RBI cybersecurity requirements and the DPDP Act when planning how information is protected and how security incidents are handled. Standards such as ISO 27001 and PCI DSS may also form part of the control framework, depending on the services and data involved.
These requirements have a technical side. Authentication, access permissions, encryption, logging and vulnerability management all contribute to meeting security expectations. The controls should also be supported by records that show they are being used and reviewed.
For example, an access review should leave evidence of what was checked and what changed. Security testing should have documented findings and remediation. Logs should be available when an incident needs to be investigated.
This makes compliance part of the normal security process rather than a separate exercise carried out only before an audit.
Security Testing and Vulnerability Management
Testing a core banking application requires some planning because the application cannot be treated like an ordinary test environment. It may be handling live transactions and supporting several connected services.
Testing should cover areas where application weaknesses can have a direct effect. APIs, authentication, session handling and business logic are examples. A vulnerability in any of these areas may give an attacker a way to misuse a legitimate application function.
Some testing can take place during development. Code analysis and security checks within the development process give teams an opportunity to deal with problems before a release reaches production. Further testing can then be carried out on deployed applications and their connected interfaces.
What happens after a vulnerability is found matters just as much. The finding needs to be assessed, assigned to the right team and fixed within an appropriate timeframe. A retest can then confirm whether the weakness has actually been addressed.
For a core banking environment, this process needs to fit operational requirements. Testing can be planned in controlled windows where necessary, with safeguards in place to avoid unnecessary disruption to transaction processing.
How Banks Can Strengthen Security Without Causing Downtime
A core banking application cannot simply be stopped whenever a security team wants to make a change. Transactions may be running, other applications may be connected to the platform, and customers may be using banking services at the same time.
That has to be considered before a security update goes into production. The team needs to know what the change touches, what depends on it and how the application will behave after the change.
Testing is therefore a major part of the process. It gives the team an opportunity to identify problems before a security change reaches the wider production environment.
Phased Security Deployment
Security changes do not all need to be released together.
A bank can start with one application component, a particular interface or a controlled group of systems. The change can then be observed before it is extended further. If something behaves differently from what was expected, the team has a smaller change to investigate.
This is useful when working with older core banking platforms. Their dependencies may not always be obvious, especially when the platform has been connected to other applications over several years.
The same thinking applies to security fixes. A vulnerability may need immediate attention, but the fix still needs to be tested against the functions that depend on the affected component. Larger changes can be scheduled alongside established release and maintenance windows.
Keeping these stages separate also makes troubleshooting easier. If several controls are changed at the same time and something goes wrong, finding the cause becomes much harder.
Non-Intrusive Monitoring and Response
Monitoring can take place while the banking application continues to process transactions. Application logs, access attempts and unusual activity can be collected without asking users to stop using the service.
What matters is what the monitoring is looking for. A sudden increase in failed authentication attempts, unusual access to a sensitive function or activity that does not match normal application behaviour can give the security team something to investigate.
Runtime protection and behaviour-based detection can add another layer of visibility. These controls are particularly useful when regular interruption of the core platform is not practical.
Response also needs to be proportionate. An unusual event may require investigation first. A compromised account might need to be restricted, while a suspicious request to an application interface may need to be blocked. The response depends on what the monitoring has identified.
This allows security teams to investigate and respond to suspicious activity while keeping normal banking operations running.
A core banking security strategy has to work across development, operations and technology teams. It also needs clear ownership. When security decisions sit with one team alone, issues around application changes, operational impact or cost can easily be missed.
The CTO has to look at how security fits with the technology roadmap. New digital services, APIs and cloud platforms should be considered when the security architecture is planned, rather than added later after the connections are already in place.
There is a financial side to the decision as well. For a CFO, an application security problem can mean more than the cost of fixing a vulnerability. Downtime, fraud, regulatory penalties and the cost of recovering from an incident can all have a direct financial impact.
That makes the choice of security controls a practical management decision. Continuous monitoring, phased changes and security testing during development can reduce some of the pressure that comes with securing a system that has to remain available.
Technology will also continue to change. AI-based threat detection, application-level Zero Trust and security by design are already becoming part of discussions around core banking modernisation. Continuous risk assessment is also more useful than waiting for a periodic review to reveal that the environment has changed.
A stronger strategy, therefore, needs to be maintained rather than written once and left unchanged. As applications, integrations and threats change, the security controls around the core platform need to be reviewed with them.
Building a Stronger Core Banking Security Strategy
A core banking security strategy has to work across development, operations and technology teams. It also needs clear ownership. When security decisions sit with one team alone, issues around application changes, operational impact or cost can easily be missed.
The CTO has to look at how security fits with the technology roadmap. New digital services, APIs and cloud platforms should be considered when the security architecture is planned, rather than added later after the connections are already in place.
There is a financial side to the decision as well. For a CFO, an application security problem can mean more than the cost of fixing a vulnerability. Downtime, fraud, regulatory penalties and the cost of recovering from an incident can all have a direct financial impact.
That makes the choice of security controls a practical management decision. Continuous monitoring, phased changes and security testing during development can reduce some of the pressure that comes with securing a system that has to remain available.
Technology will also continue to change. AI-based threat detection, application-level Zero Trust and security by design are already becoming part of discussions around core banking modernisation. Continuous risk assessment is also more useful than waiting for a periodic review to reveal that the environment has changed.
A stronger strategy, therefore, needs to be maintained rather than written once and left unchanged. As applications, integrations and threats change, the security controls around the core platform need to be reviewed with them.
Conclusion
Keeping a core banking application secure is a continuous job. There is no single security control that solves the problem, particularly when an older core platform is connected to APIs, cloud services, digital banking channels and third-party systems.
Some improvements can be made during development. Others need to happen around the live application, through access controls, monitoring, testing and careful management of connected services. Legacy systems may need a different treatment from newer applications, but they still need to be covered by the wider security setup.
The difficult part is making these changes without affecting transactions and customer access. That is why testing, monitoring and controlled deployment matter so much in a banking environment. A security fix that creates an operational problem can introduce a different kind of risk.
Core banking security should therefore be reviewed as the environment changes. New integrations, application updates, cloud services and changes in access can all alter the risk around the platform.
For banks, the focus should remain on finding weaknesses early, limiting unnecessary access and having enough visibility to respond when something unusual happens, while keeping the services customers depend on available.
Frequently Asked Questions
How can banks secure core banking applications without causing downtime?
Start with the changes that can be made without touching live transaction processing. Security checks can be added during development, suspicious activity can be monitored while the application is running, and larger changes can be introduced in smaller stages. Before a change is rolled out more widely, the team can check its effect on the core application and the services connected to it.
What are the biggest security risks in core banking applications?
There are several areas worth watching closely. Stolen credentials can lead to account takeover, while weak authentication can give attacker access that should have been restricted. APIs create another area of exposure, particularly when they connect to the core platform with mobile applications, fintech services or other systems. Application logic can also be abused, such as changing transaction limits or finding a way around a verification step.
What security controls are essential for core banking systems?
The controls will depend on the application, its architecture and the services connected to it. Strong authentication and sensible access permissions should be in place for users and services. APIs need their own security controls, and sensitive information needs appropriate encryption. Security testing during development, application logging and ongoing monitoring are also useful because they cover different stages of the application’s life.
How does Zero Trust improve core banking security?
A user being inside the bank’s network should not be enough to grant access to a sensitive banking function. Zero Trust applies checks to the access request itself and limits permissions according to what is actually required. This is particularly useful when employees, applications, APIs and external services all interact with the same core platform.
How can banks protect legacy core banking applications?
An older platform may not support every security control that is available in a newer application. That does not mean the platform has to be replaced immediately. Access restrictions, stronger authentication, encryption, monitoring and controls around connected interfaces can reduce exposure while modernisation work continues. The important part is knowing where the older system is weak and putting suitable protection around those areas.