HomeBlogGovernance and ComplianceSecurity Transformation Case Study: ISO 27001 Implementation and SOC 2 Type 2 Certification with vCISO Governance
Security Transformation Case Study: ISO 27001 Implementation and SOC 2 Type 2 Certification with vCISO Governance
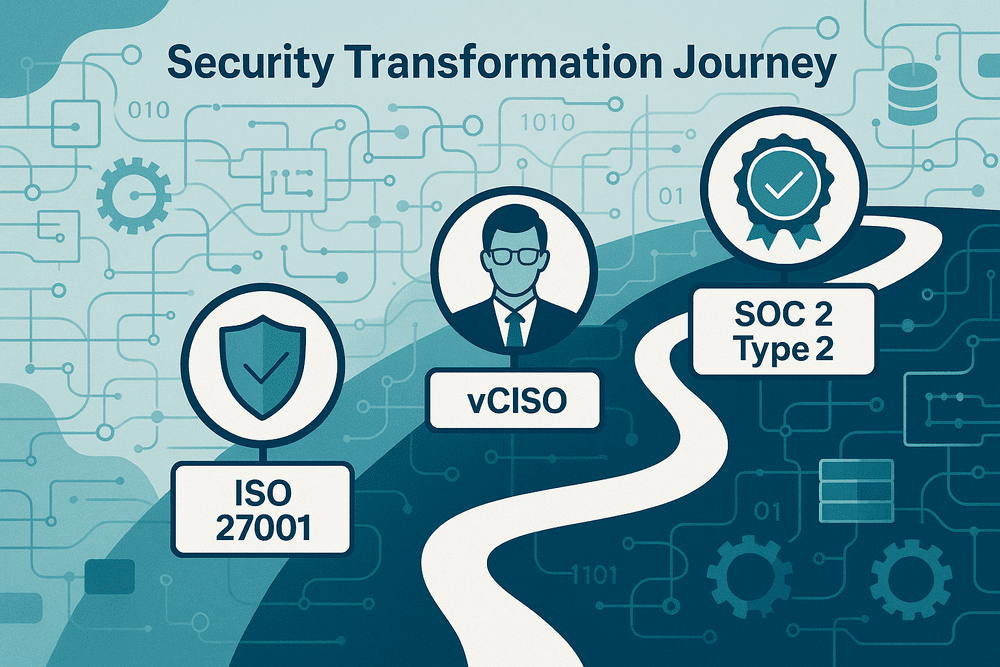
Overview
Kalp Systems supported a leading intelligent automation company that delivers a unified platform integrating Robotic Process Automation, Artificial Intelligence, Business Process Management, and low-code process automation. Serving enterprise clients across finance, healthcare, insurance, and logistics sectors, the organisation required a structured security transformation to meet growing customer and investor expectations.
With increasing demand for globally recognised compliance standards, the company initiated a multi-phase security journey focused on implementing ISO 27001, establishing vCISO governance, and obtaining SOC 2 Type 2 certification.
Client Profile
Client: Intelligent Automation Company, Name Withheld for Confidentiality
Industry: Information Technology and Services
Employees: 270
Revenue: USD 1.8 Million
Locations in Scope: Ahmedabad and Mumbai, India
Engagement Duration: 2022 to Ongoing
Business Challenges
As a rapidly growing technology organisation, the company faced several strategic security and compliance challenges.
No Formal Information Security Management System
The organisation did not have a structured Information Security Management System aligned with ISO 27001. Security practices existed but were not standardised, documented, or audit-ready.
Increasing Enterprise Compliance Requirements
Enterprise clients and investors required recognised certifications such as ISO 27001 and SOC 2 Type 2 as part of vendor onboarding and due diligence processes.
Lack of Dedicated Security Leadership
The organisation required executive-level security oversight and governance without appointing a full-time internal Chief Information Security Officer.
Multi Location Governance
Ensuring consistent control implementation and monitoring across Ahmedabad and Mumbai operations required a unified governance approach.
Sustained Control Performance for SOC 2 Type 2
SOC 2 Type 2 required continuous demonstration of control effectiveness across a defined reporting period, not just point-in-time compliance.
Our Security Transformation Approach
Kalp Systems implemented a phased and scalable security roadmap aligned with business growth objectives and international compliance standards.
Phase 1 – ISO 27001 Implementation
In 2022, Kalp Systems designed and implemented a comprehensive Information Security Management System aligned with ISO 27001 requirements.
Key activities included:
- Enterprise-wide risk assessment and risk treatment planning
- Development of security policies and procedures
- Control implementation across technology and operational environments
- Internal audit and management review support
- Stage 1 and Stage 2 audit coordination
The organisation successfully achieved ISO 27001 certification with no major non-conformities.
Phase 2 – vCISO Governance Engagement
In 2023, Kalp Systems deployed a virtual Chief Information Security Officer model to provide ongoing strategic oversight and governance.
The vCISO engagement included:
- Enterprise risk management oversight
- Compliance tracking and continuous improvement monitoring
- Vendor risk assessments and third-party security reviews
- Incident response supervision
- Executive and board-level reporting
- Security roadmap planning and maturity tracking
This engagement ensured sustained governance and leadership without requiring a full-time internal CISO.
Phase 3 – SOC 2 Type 2 Certification
In 2025, Kalp Systems led the SOC 2 Type 2 readiness and audit support programme aligned with the AICPA Trust Services Criteria.
Activities included:
- Control mapping between ISO 27001 and SOC 2 requirements
- Evidence collection and documentation validation
- Internal control testing across the reporting period
- Audit coordination and remediation support
The organisation completed its SOC 2 Type 2 audit with consistent control performance documented throughout the audit period.
Phase 4 – HIPAA Security and Privacy Alignment
As the platform began supporting healthcare and life sciences customers, the organisation needed to ensure that its security practices were aligned with HIPAA requirements for handling Protected Health Information.
Kalp Systems worked with the client to review how healthcare-related data moved across the platform and to align existing controls with the HIPAA Security Rule. The focus was on strengthening safeguards around PHI handling while building operational readiness for working with regulated healthcare organisations.
Key activities included:
- Mapping existing ISO 27001 security controls to the HIPAA Security Rule
- Reviewing data flows involving Protected Health Information across systems
- Strengthening safeguards for the storage, processing, and transmission of PHI
- Preparing operational readiness for Business Associate Agreement requirements
- Enhancing incident response procedures to address potential PHI breach scenarios
This phase helped the organisation confidently support healthcare clients while improving the protection of sensitive health data across its platform.
Phase 5 – ISO 42001 AI Governance Framework
Because the client’s platform includes Artificial Intelligence capabilities, the organisation also began preparing a governance framework aligned with ISO 42001.
The objective of this phase is to introduce stronger oversight for AI-driven features within the platform. By establishing governance around how AI models are developed, monitored, and managed, the organisation aims to ensure responsible and secure use of AI technologies as part of its long-term security strategy.
Key activities included:
- Establishing an AI governance framework aligned with ISO 42001 principles
- Defining risk management processes for AI-based automation and decision systems
- Introducing controls for model lifecycle governance and ongoing monitoring
- Creating transparency and accountability mechanisms for AI-driven services
- Developing internal guidelines for responsible and secure AI deployment
This initiative strengthens the organisation’s ability to manage AI-related risks while supporting innovation within its automation platform.
Phase 6 – Digital Personal Data Protection (DPDP) Act Compliance
With the introduction of India’s Digital Personal Data Protection Act, the organisation also began preparing its data protection practices to align with upcoming regulatory requirements.
Kalp Systems is supporting the client in strengthening privacy governance and ensuring that personal data processing activities meet the expectations of the DPDP framework.
Key activities included:
- Creating a personal data inventory and mapping how data moves across systems
- Designing a consent management framework for personal data processing
- Establishing processes to manage data principal rights requests
- Preparing breach notification procedures aligned with DPDP requirements
- Reviewing vendor and third-party data processing practices
These efforts help the organisation prepare for India’s evolving data protection regulations while strengthening overall privacy governance across its digital services.
Measurable Results
The security transformation delivered clear and measurable outcomes:
- Successfully obtained ISO 27001 and SOC 2 Type 2 certifications following rigorous external audits and structured control validation
- 30 per cent improvement in incident response time across both locations
- Sustained executive-level security governance through vCISO engagement
- Enhanced stakeholder confidence in the organisation’s security posture
- Faster enterprise procurement cycles due to improved compliance assurance
Long-Term Business Impact
Through ISO 27001 implementation, continuous vCISO governance, and SOC 2 Type 2 certification, the organisation transitioned from informal security practices to a structured, globally aligned compliance framework.
This transformation strengthened enterprise trust, improved operational resilience, and positioned the company for secure and scalable growth.
Kalp Systems continues to support the organisation in its ongoing security maturity journey.