HomeBlogCyber Security AwarenessCyber Security Explained in Simple Terms for Business Leaders
Cyber Security Explained in Simple Terms for Business Leaders
Introduction
Cybersecurity is essential for every modern organisation. It protects sensitive business information, customer data, financial records, and digital systems from cyber attacks and data breaches. When security fails, the consequences can include financial losses, legal penalties, reputational damage, and loss of customer trust.
However, many business leaders find cybersecurity difficult to understand because it is often explained using highly technical terms. Concepts such as firewalls, encryption, access control, vulnerabilities, and patches can feel overwhelming if you do not come from a technical background.
The good news is that cybersecurity does not have to be complicated. In reality, the principles behind cybersecurity are very similar to something every business leader already understands very well: physical security.
Why Cyber Security Feels Complex for Many Leaders
Cybersecurity feels complicated mainly because the digital threat landscape constantly evolves. As technology advances, attackers develop new techniques to exploit weaknesses in systems and human behaviour. This makes it difficult for organisations to keep up with the latest threats and best practices.
Another reason is that security discussions are often led by technical teams. Business leaders may receive reports filled with technical metrics instead of clear explanations of risk and business impact. This communication gap creates confusion and sometimes delays important security decisions.
To simplify the topic, let us look at cybersecurity from a familiar perspective. Imagine you are protecting confidential documents inside your office building.
Cyber Security Explained Through a Physical Security Example
Imagine your organisation stores highly confidential documents inside its office. These documents could represent client data, contracts, financial statements, strategic plans, or intellectual property. Naturally, you would not leave them exposed or accessible to anyone walking by.
To protect these documents, you would implement multiple layers of security. You would secure the entrance, control who enters different rooms, lock the documents safely, and replace any faulty locks when necessary.
Cybersecurity works in the same way. Let us break it down step by step.
Firewall Is Like a Security Guard at the Office Entrance
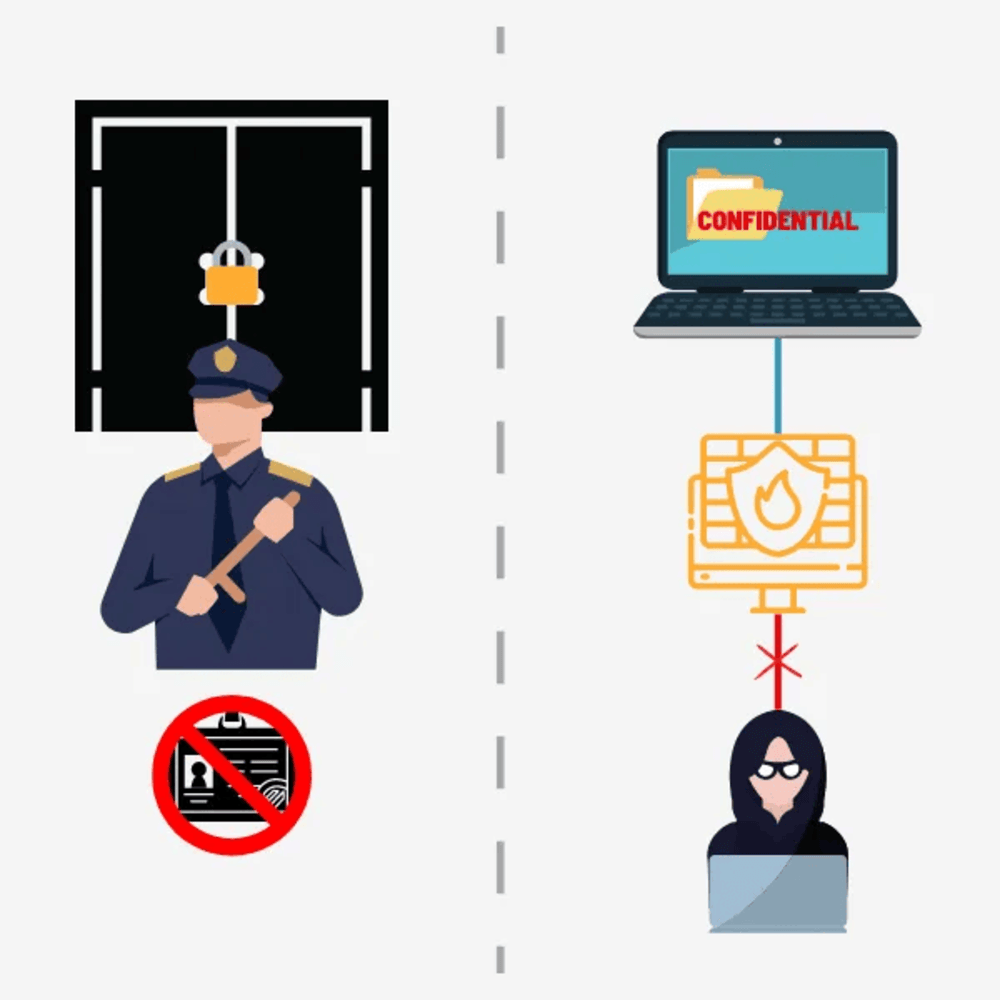
The first step in protecting your office is preventing unauthorised individuals from entering the premises. You would secure doors and windows and possibly appoint a security guard at the entrance. The guard checks identity cards and decides who should be allowed inside.
In the digital world, a firewall acts as that security guard. It monitors incoming and outgoing network traffic and blocks suspicious or unauthorised connections. Just like a guard prevents strangers from walking into your building, a firewall prevents malicious traffic from entering your organisation’s network.
Additionally, computer systems have digital entry points known as ports. If left open unnecessarily, these ports can be exploited by attackers. A properly configured firewall can close unused ports, reducing the chances of unauthorised access.
Access Management Is Like Controlling Which Employees Can Enter Certain Rooms
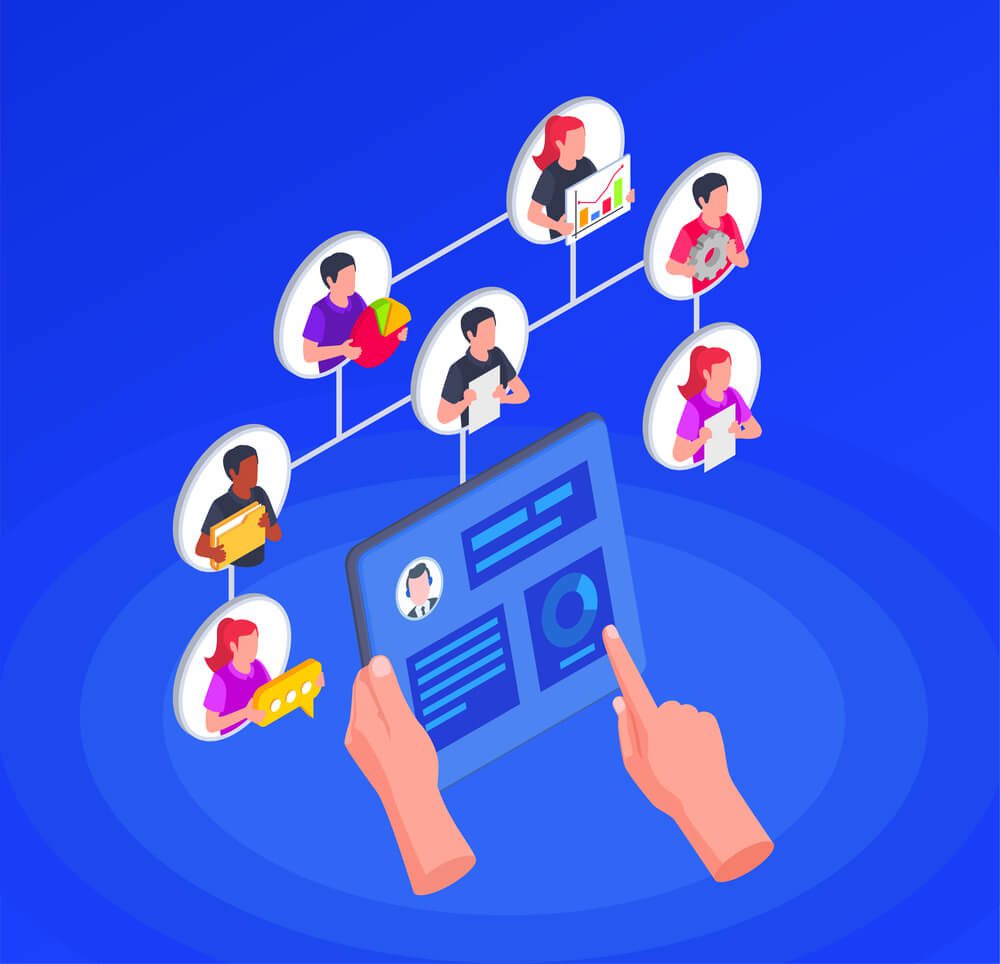
Now imagine that someone has successfully entered the building. That does not mean they should have access to every office, archive room, or executive cabin. Most organisations follow a hierarchy where access is granted based on role and responsibility.
This concept is known in cybersecurity as Identity and Access Management. It ensures that employees can only access the systems and data required to perform their job functions. This principle is often referred to as least privilege.
By limiting access, organisations reduce the risk of internal misuse, accidental data exposure, and insider threats. Even if a cyber attacker gains entry using stolen credentials, restricted access helps limit the damage.
Password Protection Is Like Locking Confidential Files in a Cabinet
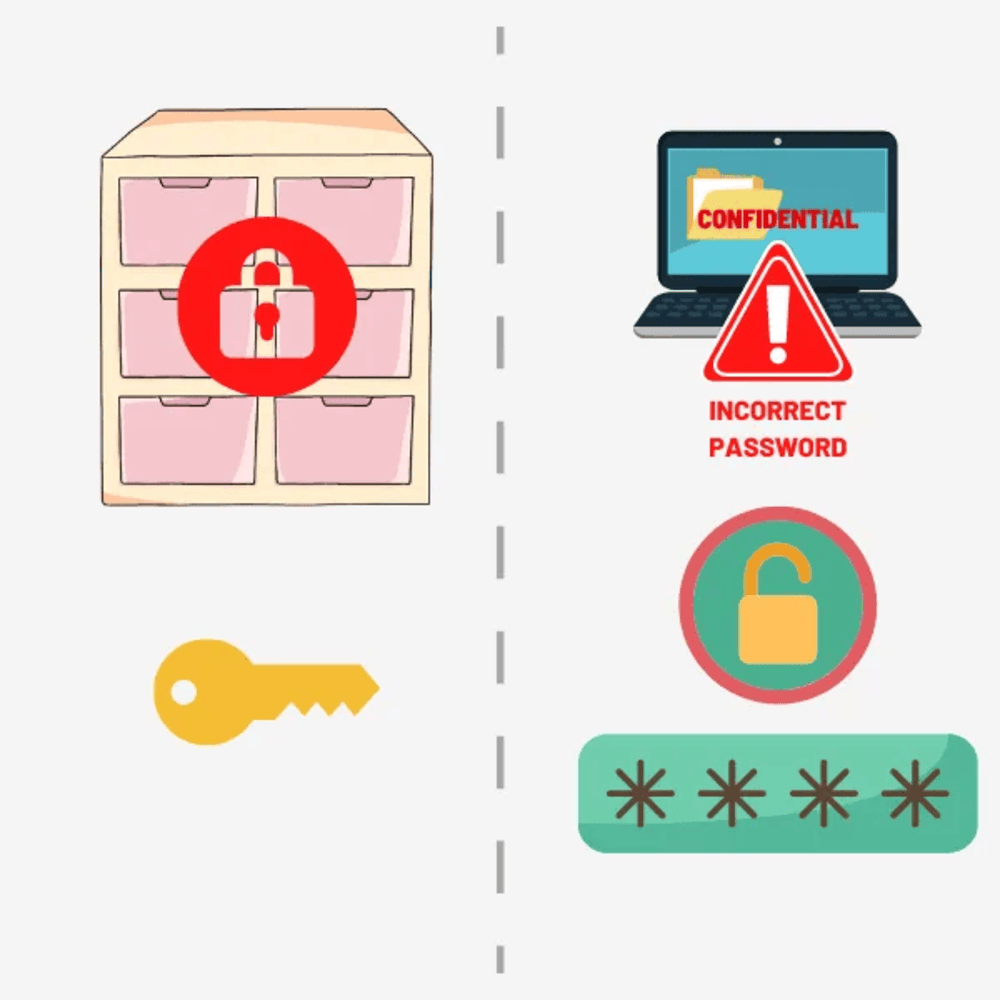
Even with secured entrances and controlled access, sensitive documents should not be left on open desks. They are usually stored inside locked cabinets, and only authorised individuals hold the key.
In cybersecurity, passwords serve as those locks. A strong password makes it significantly harder for attackers to gain access to files, systems, and applications. Weak passwords, on the other hand, are like fragile locks that can be easily broken.
For stronger protection, organisations often use multi-factor authentication. This adds a layer of verification, such as a one-time code sent to a mobile device. The stronger the authentication mechanism, the more secure your digital assets become.
Software Updates Are Like Replacing Weak or Faulty Locks
Let us say the manufacturer of your office locks informs you that a defect has been discovered. The lock can now be opened easily by intruders. They offer to replace it with an improved and secure version. Ignoring this warning would put your office at serious risk.
Similarly, software vendors regularly discover vulnerabilities in their products. When they release security patches or updates, they are essentially replacing weak locks with stronger ones. Failing to apply updates leaves systems exposed to known threats.
Many cyber attacks succeed not because security solutions are missing, but because available updates were not installed in time. Keeping software and operating systems up to date is a simple yet powerful protective measure.
The Power of a Multi-Layered Security Approach
Notice something important in this example. You did not rely on just one security control. You secured the entrance, controlled internal access, locked documents, and replaced faulty locks when needed.
Cybersecurity follows the same principle, often called defence in depth. No single solution can guarantee complete protection. A firewall alone is not enough. Strong passwords alone are not enough. Access control alone is not enough.
When multiple layers work together, the organisation becomes significantly more resilient. Even if one layer fails, another layer can prevent or limit damage.
Why This Matters for Business Leaders
Business leaders are responsible for protecting the organisation’s assets, reputation, and long-term sustainability. Cybersecurity is not just an IT concern. It is a business risk management issue.
Understanding these basic concepts helps leaders:
- Make informed investment decisions
- Evaluate security proposals confidently
- Support regulatory compliance efforts
- Protect customer trust
- Ensure operational continuity
When leaders understand cybersecurity in simple and practical terms, they can bridge the gap between technical teams and strategic decision-making.
Conclusion
Cybersecurity may seem technical on the surface, but its foundation is straightforward. It is about protecting valuable assets through layered security controls, just as you would protect confidential documents in a physical office.
By viewing cybersecurity through the lens of physical security, business leaders can better understand firewalls, access management, password protection, and software updates without needing deep technical expertise.
The goal is simple. Protect what matters most. With the right layered approach and informed leadership, cybersecurity becomes a structured, practical, and strategic part of business success.
Frequently Asked Questions
What is cybersecurity in simple terms?
Cybersecurity is the practice of protecting digital systems, networks, and data from unauthorised access, theft, damage, or disruption. In simple terms, it is the digital equivalent of locking doors, checking identities, and safeguarding valuable business assets.
Why is cybersecurity important for business leaders?
Cybersecurity directly affects financial stability, regulatory compliance, operational continuity, and brand reputation. Business leaders must understand it to make informed decisions about risk management, investments, and long-term strategic planning.
What are the basic components of cybersecurity?
Some core components include firewalls, access management, strong password policies, multi-factor authentication, software updates, data backups, and continuous monitoring. These elements work together to create layered protection.
How often should software and systems be updated?
Software and operating systems should be updated as soon as security patches are released. Delayed updates leave known vulnerabilities exposed and increase the risk of attack.
Is cybersecurity only the responsibility of the IT department?
No. While IT teams manage technical controls, cybersecurity is a shared responsibility. Leadership plays a critical role in defining policies, allocating budgets, promoting security awareness, and ensuring organisational accountability.