HomeBlogCyber Incidents and AttacksThe Evolution of Cyber Threats: What Businesses Must Know
The Evolution of Cyber Threats: What Businesses Must Know
Introduction
Cyber threats are no longer just an IT issue. They sit much closer to business risk than most organisations realise. One incident can slow down operations, affect customers, and in some cases, stop work completely.
If you look at how cyber threats have changed over time, the shift is quite clear. Earlier, they were more about experimentation. Now, they are structured, targeted, and in many cases, built purely for financial gain. For businesses, understanding this shift is not about theory. It helps in making better decisions before something goes wrong.
What Are Cyber Threats and Why Businesses Should Care
At a basic level, cyber threats are attempts to access systems or data without permission. But in a business context, the definition does not matter as much as the impact.
Types of Cyber Threats
Most businesses deal with a mix of issues rather than a single type of threat:
- Malware and ransomware that affect systems directly
- Phishing attempts that target employees
- DDoS attacks that slow things down or take services offline
- Insider risks, which are often overlooked
These are not rare scenarios. They are part of day-to-day risk now.
Business Impact of Cyber Attacks
What usually gets underestimated is how far the impact spreads:
- Work stops, which means revenue is affected
- Customers lose confidence faster than expected
- Compliance issues start showing up
- Internal data may no longer be reliable
So the question is not whether cybersecurity matters. It is a measure of how prepared the business is.
The Early Days of Cyber Threats
If you go back a few decades, cyber threats looked very different. They were smaller, slower, and often not driven by money.
The First Known Threats
Early examples like the Creeper virus or the Morris Worm were not created with business disruption in mind. Still, they showed something important, systems could be reached and affected from the outside.
That idea, even at a small scale, changed how people looked at computer security.
Rise of Early Hackers
As systems became more accessible, more people started testing boundaries:
- Some were just curious
- Some wanted recognition
- Some were trying to prove weaknesses
At that stage, it did not feel like organised cybercrime. But it was the starting point.
The Internet Era and Rise of Scalable Attacks
Things changed quickly once the internet became widely used. The scale increased, and so did the impact.
Emergence of Phishing Attacks
Phishing worked because it was simple and effective:
- Emails that looked genuine
- Links that led to fake pages
- Employees unknowingly share access
Even today, many attacks still begin this way. Not because systems are weak, but because people can be misled.
Spread of Malware and Botnets
At the same time, attackers started thinking bigger:
- Malware could spread across multiple systems
- Botnets allowed control of thousands of devices
- DDoS attacks could take services offline
This is where cyber threats moved from isolated cases to something businesses had to manage actively.
The Shift to Advanced and Targeted Threats
As basic security improved, attackers stopped going after everyone. They started choosing their targets more carefully.
What Are Advanced Persistent Threats (APTs)
APTs are not rushed attacks. They take time:
- Entry is usually quiet
- Movement inside systems is gradual
- Data is collected without raising alarms
These are not random attempts. They are planned.
Why APTs Are Dangerous for Businesses
The real concern with APTs is visibility:
- They do not announce themselves
- They stay longer than expected
- They focus on high-value information
In many cases, businesses realise the issue much later than they should.
The Ransomware Era and Financial Motivation
At some point, cyber attacks stopped being experimental and became commercial. Ransomware is probably the clearest example of that shift.
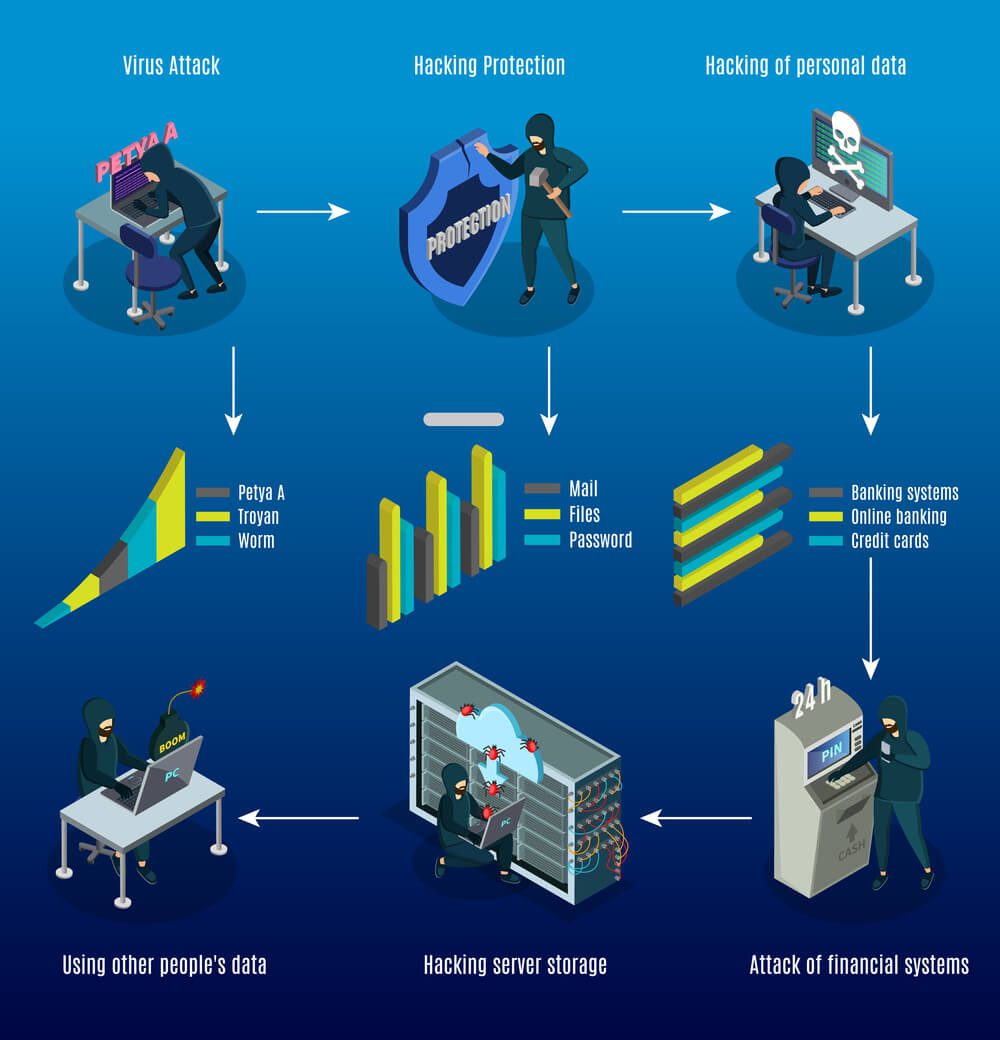
How Ransomware Works
The approach is straightforward:
- Systems or data are locked
- Access is restricted
- Payment is demanded
But the impact is not simple. It creates pressure almost immediately.
Evolution of Ransomware Attacks
Ransomware has become more aggressive over time:
- Data is also threatened to be exposed
- Tools are available for anyone willing to use them
- Businesses are chosen deliberately
It is no longer random. It is calculated.
Emerging Cyber Threats Businesses Must Watch
New technologies bring new risks. That part has not changed. What has changed is how quickly these risks show up.
IoT and Connected Device Risks
With more devices connected:
- Entry points increase
- Security is not always consistent
- Networks become harder to control
It creates small gaps that are easy to miss.
AI-Driven Cyber Attacks
AI is now part of the picture:
- Attacks can be automated
- Patterns can be analysed faster
- Messages can look more convincing
This makes traditional detection less reliable.
Cybersecurity Challenges and How Businesses Can Respond
The challenge is not just the number of threats. It is the speed at which they change.
Key Cybersecurity Challenges
Some issues show up again and again:
- Teams are not always fully aware
- Systems become complex over time
- Threats evolve faster than processes
- Detection is not always immediate
This is where gaps start forming.
Practical Security Measures
What helps is not always complicated:
- Keeping systems updated
- Managing access properly
- Training people regularly
- Watching for unusual activity
Consistency matters more than complexity here.
Key Takeaways for Business Leaders
At a leadership level, cybersecurity decisions often get delayed. Usually, until something happens.
Strategic Priorities for Businesses
A few things make a real difference:
- Treat cybersecurity as part of business planning
- Spend on prevention, not just recovery
- Review risks more often than you think is needed
These are not one-time actions.
Building a Security-First Culture
Technology alone is not enough:
- People need to understand risks
- Basic practices should be followed daily
- Responsibility should not sit with one team
Culture plays a bigger role than expected.
Conclusion
Cyber threats have not just increased; they have changed in nature. They are more structured, more targeted, and more connected to financial outcomes than before.
For businesses, the focus should shift from reacting to preparing. Understanding how these threats have evolved is a good starting point. Acting on that understanding is what actually reduces risk.
Frequently Asked Questions
What are cyber threats in simple terms?
Cyber threats are attempts to access or damage systems and data without permission. They can disrupt normal business operations or expose sensitive information.
Why are cyber threats increasing?
As more business activities move online, the opportunities for attackers increase. At the same time, tools used for attacks have become easier to access.
What is the most common cyber threat for businesses?
Phishing and ransomware are among the most common threats because they are effective and do not always require complex methods.
How can businesses protect themselves from cyber attacks?
Basic steps like strong authentication, regular updates, employee awareness, and monitoring systems can reduce most risks.
What is ransomware in cybersecurity?
Ransomware is an attack where data is locked or taken, and payment is demanded to restore access or prevent it from being shared.